Security & data
What moves, and what doesn't.
A hosted assistant that reads your ERP has to be specific about this, so here it is in full: what stays in your system, what reaches ours, how long we hold it, and the one requirement that decides whether FAC Chat will work for you at all.
-
You ask, on your own site
FAC Chat signs the request and sends the question out. your site
-
FAC Cloud works out what to do
The model runs here, on our servers. This is the part you subscribe to. hosted by us
-
The tool runs back in your database
We connect back into your site with a token belonging to the person who asked, so the change is made by them, in your audit log. your site
Before the detail
Four things a buyer needs before anything else on this page. Restated here for scanning — the detail below is where each one is proven.
Where your ERP data stays
Your records, conversation history, audit trail and permissions never leave your own site. The assistant asks for one record at a time, as the person who asked.
What reaches FAC Cloud
Each question and what it turns up, anything you upload or attach, what the assistant remembers, and your workflow history.
What we keep, and for how long
Knowledge-base documents and memories until you delete them. Workflow step history for 30 days, run history for 90 — then both are gone automatically.
How permissions are enforced
One person's authority at a time, rebuilt per request from what they may do, and nothing is written without approval.
Your site must be reachable from the internet
A site on localhost, or one only your office network can see, cannot be connected — we check during registration and refuse rather than let you find out later. If that rules you out, FAC Connect works the other way round: your AI client connects out to your site, so a firewalled site is fine.
What moves, and what stays
Listed because you are entitled to know it, not because it is buried in a policy.
| Your ERP records. | No table is copied to us and nothing is bulk-synced. When the assistant needs a record it asks your site for that record, at that moment, as the person who asked the question. |
|---|---|
| Your conversation history. | Chat history is written to your own database. FAC Cloud does not store transcripts of your conversations. |
| Your audit trail. | Every tool call is recorded on your site. It is your record, and we cannot change it. |
| Your permissions. | Access is granted per person, not per company. The assistant is handed one user's authority at a time and cannot exceed it. |
| Each message, as you send it. | Your question, and the page you are looking at when you ask it — including the values on the document open in front of you, which is how it knows what "this order" means. |
|---|---|
| What your question turns up. | The records the assistant fetched to answer you pass through our servers on the way to the model. That is unavoidable in any hosted assistant, and it is why we are specific about the rest of this page. |
| Documents you upload. | Anything you add to the knowledge base is stored on FAC Cloud, not on your site — the file, its text and its search index. There is no local copy; deleting it here deletes it. |
| Images you attach to a message. | A photograph or screenshot you attach is sent as an image, not as extracted text, because that is how it is read. The picture reaches FAC Cloud and the model provider along with the question. A text-bearing document has its text extracted on your site first, and only the text is sent. |
| What the assistant remembers. | Long-term memories are written and stored on FAC Cloud. You can read, edit and delete them. |
| Workflow history. | When a workflow runs, what each step received and produced is stored on FAC Cloud so you can see why it did what it did. |
| Access to your site. | So we can act on your behalf, we hold a token for each user who connects, encrypted. Revoke it on your own site at any time and the access ends with it. |
| Your account. | Who your users are, what they spent, and the billing details on your invoice. |
How long we keep it
| Item | Kept for | What happens | Where it is stored |
|---|---|---|---|
| Conversation transcripts. | Not stored on our servers. | Your database holds them. | Your own site. |
| Knowledge-base documents. | Until you delete them. | Stored on FAC Cloud. | Hosted by us — India and other regions. |
| Long-term memories. | Until you delete them. | Stored on FAC Cloud. | Hosted by us — India and other regions. |
| Workflow step history. | 30 days. | Deleted automatically. | Hosted by us — India and other regions. |
| Workflow run history. | 90 days. | Deleted automatically. | Hosted by us — India and other regions. |
| Usage and billing records. | As long as tax law requires. | See the Privacy Policy. | Hosted by us — India and other regions. |
The model providers
We do not train on your data
Not our models, not anyone else's. We use enterprise provider terms that exclude your content from training.
The keys are ours, not yours
You do not manage model keys or provider accounts. If you would rather hold them yourself, that is what FAC Connect is for.
| Sub-processor | What it does | Where it processes | Their commitment |
|---|---|---|---|
| Anthropic, PBC. | LLM inference (Claude models) — receives your prompts, conversation context, system instructions and any memories or knowledge it draws on. | United States. | Anthropic API / Claude for Work — no training on customer inputs or outputs. |
| OpenAI, Inc. | LLM inference (GPT and o-series models) — receives your prompts, conversation context, system instructions and any memories or knowledge it draws on. | United States. | OpenAI Enterprise Privacy — no training on business data. |
| Amazon Web Services, Inc. (Amazon Bedrock). | LLM inference via Amazon Bedrock — receives your prompts, conversation context, system instructions and any memories or knowledge it draws on. | United States, and other AWS regions as configured. | AWS Service Terms for Amazon Bedrock — inputs and outputs are not used to train AWS or third-party models. |
| Google LLC (Vertex AI). | LLM inference (Gemini models) — receives your prompts, conversation context, system instructions and any memories or knowledge it draws on. | United States, and other Google Cloud regions as configured. | Google Cloud / Vertex AI data governance — customer data is not used to train Google's foundation models. |
| Stripe, Inc. / Stripe India. | Global payment processing — receives billing email, country and tokenised payment-method data. | Global — Stripe regions. | PCI DSS Level 1. |
| Razorpay Software Pvt. Ltd. | India and select non-India payment processing — receives billing email, phone, country and tokenised payment-method data. | India. | RBI compliant, PCI DSS. |
| Cloud infrastructure provider(s). | Hosting of our service infrastructure — receives all Customer Personal Data the Service processes. | India, and other regions as configured. | Major-provider security certifications — ISO 27001, SOC 2. |
| Email delivery provider(s). | Transactional email — verification, invoices, alerts — receives billing and administrator email, and the content of the message. | As the provider operates. | SPF, DKIM, DMARC, TLS in transit. |
Annex B of the Data Processing Agreement is the authoritative, maintained list. If this table and Annex B ever disagree, the DPA governs.
What protects you day to day
| Nothing is written without permission. | A tool you have never approved is asked about, not run. | Default. |
|---|---|---|
| One person's authority at a time. | The tool list is rebuilt per request from what that user may do. | Per request. |
| Both ends prove who they are. | Your site signs every request; we call your site back to prove the origin is genuine. | Signed. |
| You can cut us off. | Revoke the connection on your own site and the access ends immediately. | Your call. |
Incident handling and access control
What we commit to if something goes wrong, taken from the Data Processing Agreement and the Privacy Policy — not a description softened for this page.
Access to production
Role-based access control gates who can reach production systems, and every access is logged.
If something goes wrong
A documented incident-response procedure defines roles and severity levels, run from the moment an incident is detected.
You hear about a breach
We notify you without undue delay, and where feasible within 72 hours of becoming aware.
So does the regulator
As an Indian body corporate, we report qualifying cyber incidents to the Indian Computer Emergency Response Team (CERT-In) within 6 hours of detection.
The full technical and organisational measures we commit to are set out in Annex A of the Data Processing Agreement.
See it for yourself
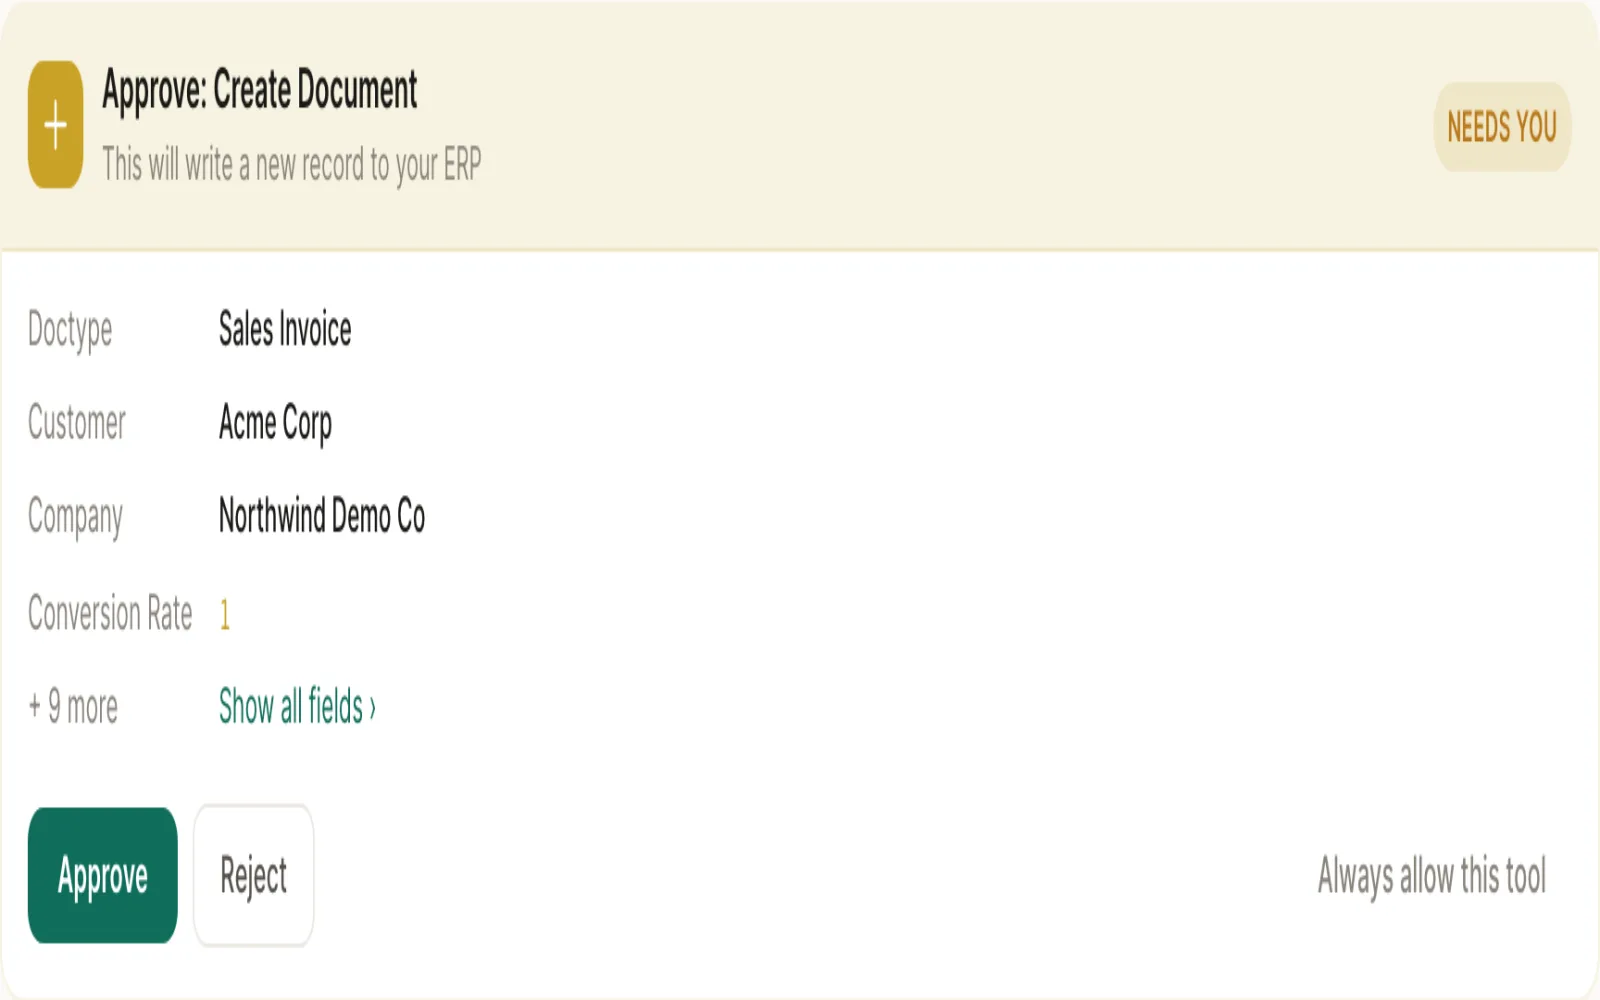
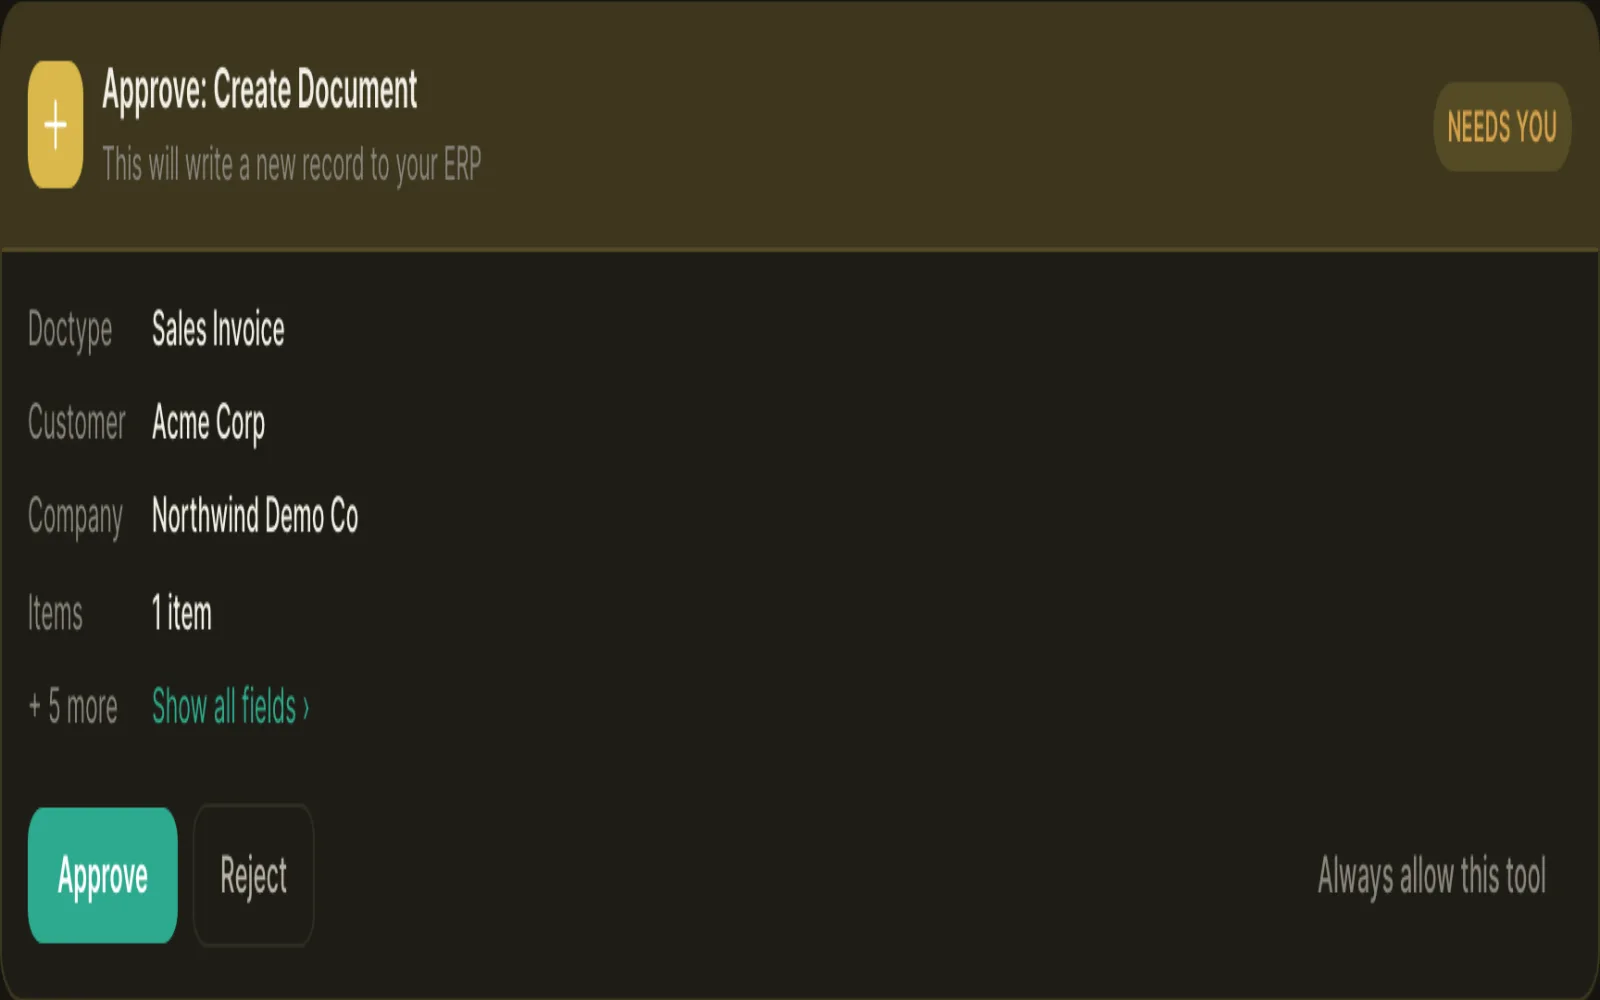
Both protections above are checkable directly, on your own site — not just stated here.
The approval card
The audit log
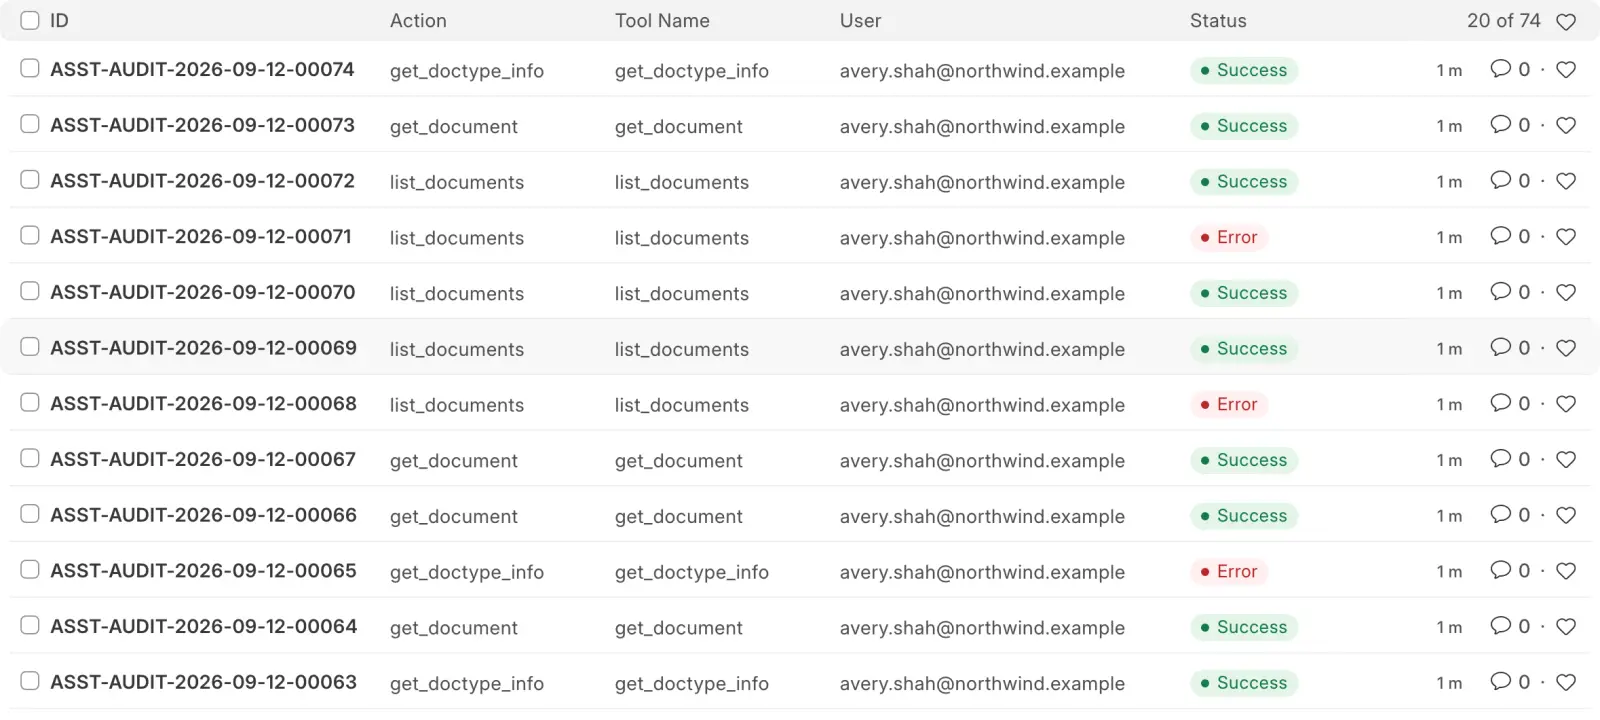
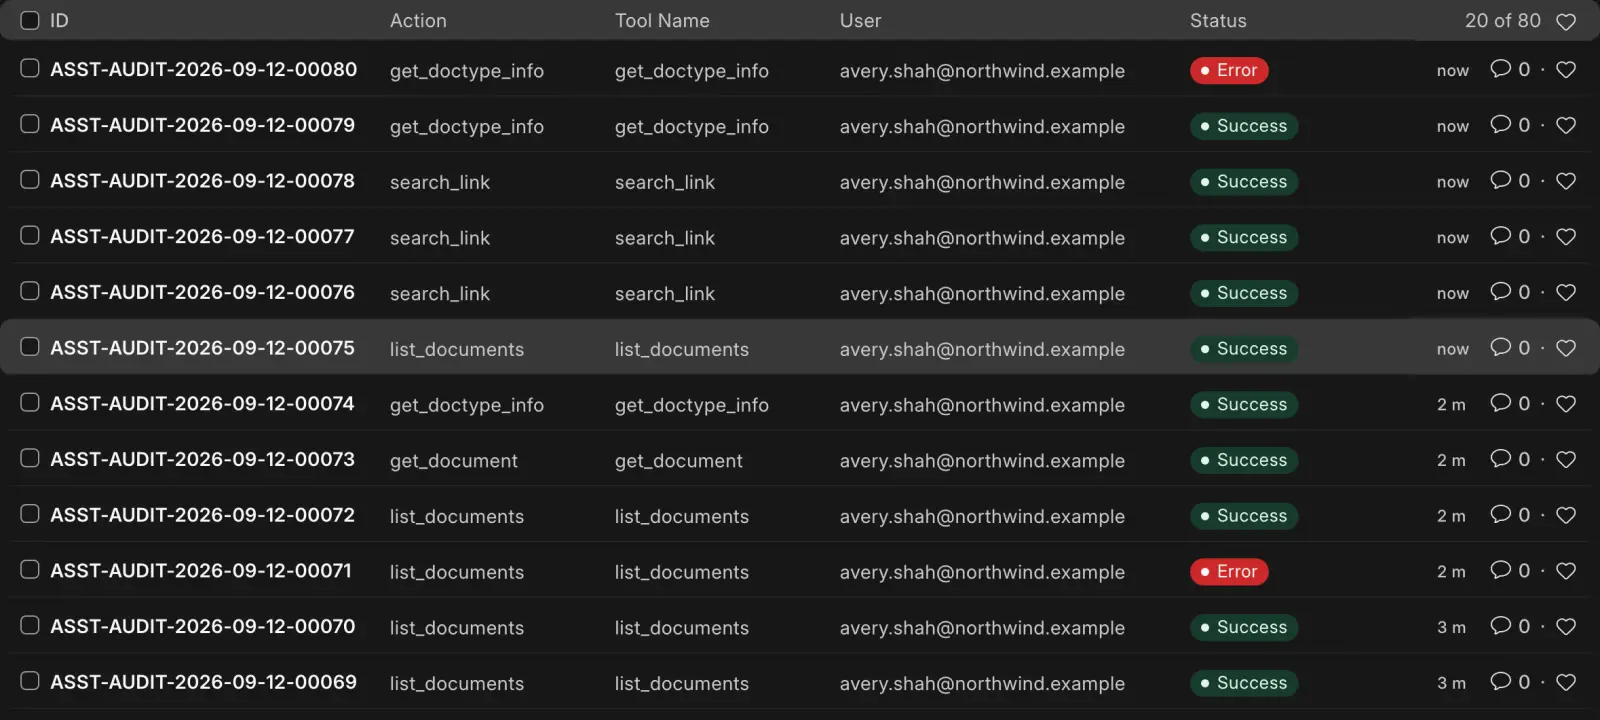
Your rights over all of it
Export, correction, erasure and restriction requests are handled across every part of the service, not just the obvious one. Write to [email protected], or to Sunitha Ravindran, our grievance officer under India's Digital Personal Data Protection Act, for complaints. Both are on the contact page.
The binding versions of all of this are the Privacy Policy and the Data Processing Agreement, which sets out our obligations as your processor.
Read it, then test it
Everything on this page is checkable from the product itself — open the audit log on your own site and watch the calls arrive under your own name. If your security review needs something we have not published, write to us and we will answer it.